Get Ready for the Future! Download the State of Checkout 2025 White Paper Today
Platform

Product & Solutions

Learn more about the only open payments platform built for global commerce

Pricing

Solutions

Open Payments Connectivity
Payment Token Ownership & Portability
Intelligent Payment Optimization
Fraud Prevention & Authentication
Operational Agility & Simplicity
Centralized Management & Reporting

Platform Pillars

Connect

The unified orchestration layer for wallets and alternative payments

Vault

The secure repository for all your payment methods

Optimize

Workflow-driven payments intelligence for smarter routing and higher auth rates

Protect

A flexible fraud and authentication layer. Instantly add advanced fraud tools and 3DS

Agentic

One integration to sell inside ChatGPT, Gemini, and every agentic platform

View How Spreedly

Connects to your favorite payment methods
Optimizes your revenue
Protects your data
Reduces fraud
View the Demo
Resources

The Open Payments Library

Take a look at all of our resources and get the information you need to grow your business

View all Resources

Featured resources

The Payments Guide to Expansion into LATAM
Accelerate Your Growth by Expanding into Brazil
Security, Compliance, and AI: Inside Spreedly’s 2025 Foundation:

Spreedly Makes Agentic Commerce a Live Channel for Merchants

Read More
Company

Support Portal

Spreedly Support
Trust Center
Platform Status

Developer Portal

Developer Guides
Documentation
Parter Integrations

Partners & Integrations

Integrations Ecosystem
Our Partners

Latest Partner News

Webinars

Paysafe Unveils Strategic Partnership with Spreedly

Featured Partner

PayPal
Product & Solutions

Product & Solutions

Learn more about the only open payments platform built for global commerce

Pricing

Solutions

Open Payments Connectivity
Payment Token Ownership & Portability
Intelligent Payment Optimization
Fraud Prevention & Authentication
Operational Agility & Simplicity
Centralized Management & Reporting

Platform Pillars

Connect

The unified orchestration layer for wallets and alternative payments

Vault

The secure repository for all your payment methods

Optimize

Workflow-driven payments intelligence for smarter routing and higher auth rates

Protect

A flexible fraud and authentication layer. Instantly add advanced fraud tools and 3DS

Agentic

One integration to sell inside ChatGPT, Gemini, and every agentic platform

View How Spreedly

Connects to your favorite payment methods
Optimizes your revenue
Protects your data
Reduces fraud
View the Demo
Pricing
Resources

The Open Payments Library

Take a look at all of our resources and get the information you need to grow your business

View all Resources

Featured resources

The Payments Guide to Expansion into LATAM
Accelerate Your Growth by Expanding into Brazil
Security, Compliance, and AI: Inside Spreedly’s 2025 Foundation:

Spreedly Makes Agentic Commerce a Live Channel for Merchants

Read More
Developers

Support Portal

Spreedly Support
Trust Center
Platform Status

Developer Portal

Developer Guides
Documentation
Integrations

Partners & Integrations

Integrations Ecosystem
Our Partners

Latest Partner News

Webinars

Paysafe Unveils Strategic Partnership with Spreedly

Featured Partner

PayPal
Company

Company

About
Leadership
Careers
Contact Us
News
Pricing
Log In
See a Demo
Log In
See a Demo
Platform

Product & Solutions

Learn more about the only open payments platform built for global commerce

Pricing

Solutions

Open Payments Connectivity
Payment Token Ownership & Portability
Intelligent Payment Optimization
Fraud Prevention & Authentication
Operational Agility & Simplicity
Centralized Management & Reporting

Platform Pillars

Connect

The unified orchestration layer for wallets and alternative payments

Vault

The secure repository for all your payment methods

Optimize

Workflow-driven payments intelligence for smarter routing and higher auth rates

Protect

A flexible fraud and authentication layer. Instantly add advanced fraud tools and 3DS

Agentic

One integration to sell inside ChatGPT, Gemini, and every agentic platform

View How Spreedly

Connects to your favorite payment methods
Optimizes your revenue
Protects your data
Reduces fraud
View the Demo
Use Cases
Resources

The Open Payments Library

Take a look at all of our resources and get the information you need to grow your business

View all Resources

Featured resources

The Payments Guide to Expansion into LATAM
Accelerate Your Growth by Expanding into Brazil
Security, Compliance, and AI: Inside Spreedly’s 2025 Foundation:

Spreedly Makes Agentic Commerce a Live Channel for Merchants

Read More
Company

Support Portal

Spreedly Support
Trust Center
Platform Status

Developer Portal

Developer Guides
Documentation
Blog
Platform

Product & Solutions

Learn more about the only open payments platform built for global commerce

Pricing

Solutions

Open Payments Connectivity
Payment Token Ownership & Portability
Intelligent Payment Optimization
Fraud Prevention & Authentication
Operational Agility & Simplicity
Centralized Management & Reporting

Platform Pillars

Connect

The unified orchestration layer for wallets and alternative payments

Vault

The secure repository for all your payment methods

Optimize

Workflow-driven payments intelligence for smarter routing and higher auth rates

Protect

A flexible fraud and authentication layer. Instantly add advanced fraud tools and 3DS

Agentic

One integration to sell inside ChatGPT, Gemini, and every agentic platform

View How Spreedly

Connects to your favorite payment methods
Optimizes your revenue
Protects your data
Reduces fraud
View the Demo
Use Cases
Resources

The Open Payments Library

Take a look at all of our resources and get the information you need to grow your business

View all Resources

Featured resources

The Payments Guide to Expansion into LATAM
Accelerate Your Growth by Expanding into Brazil
Security, Compliance, and AI: Inside Spreedly’s 2025 Foundation:

Spreedly Makes Agentic Commerce a Live Channel for Merchants

Read More
Company

Support Portal

Spreedly Support
Trust Center
Platform Status

Developer Portal

Developer Guides
Documentation
Blog
Log In
See Demo
Back to Blog
Back to News

Payment Security

August 13, 2026

The Real Cost Of PCI Compliance

PCI compliance can cost as little as $1,000 or as much as $50,000+ a year, and the gap comes down to one thing: your merchant level. Here's what sets your price, and how to keep it from creeping toward the high end.

Written by

Rachel Fine

In this article

Share

Related products

Vault

Lorem Ipsum Dolor Sit

Vel sed vitae enim nec suspendisse ut viverra tincidunt quis

Learn More

Subscribe to our blog

Get practical, actionable insights written by experts from the world of digital payment solutions delivered to your Inbox.

A cardholder data breach costs a company $4.88 million on average and takes 292 days to find and contain.

What you spend to avoid that outcome swings by six figures depending on one classification: whether the card networks treat your business as a merchant or a service provider, and how much cardholder data touches your systems.

Enterprise security leaders aren't always super enthusiastic about it. 93% of them call PCI DSS's requirements significant, and 90% doubt they can meet the compliance deadlines in front of them.

What PCI compliance costs depends on your tier

Compliance budgets scale with transaction volume and entity classification, not company size or industry.

The platform threshold trap. Merchants hit Level 1 at 6 million transactions a year. Service providers, meaning platforms and software vendors, hit Level 1 at just 300,000 transactions a year, roughly 820 a day. That threshold is twenty times stricter, and it catches platforms that think of themselves as mid-market.
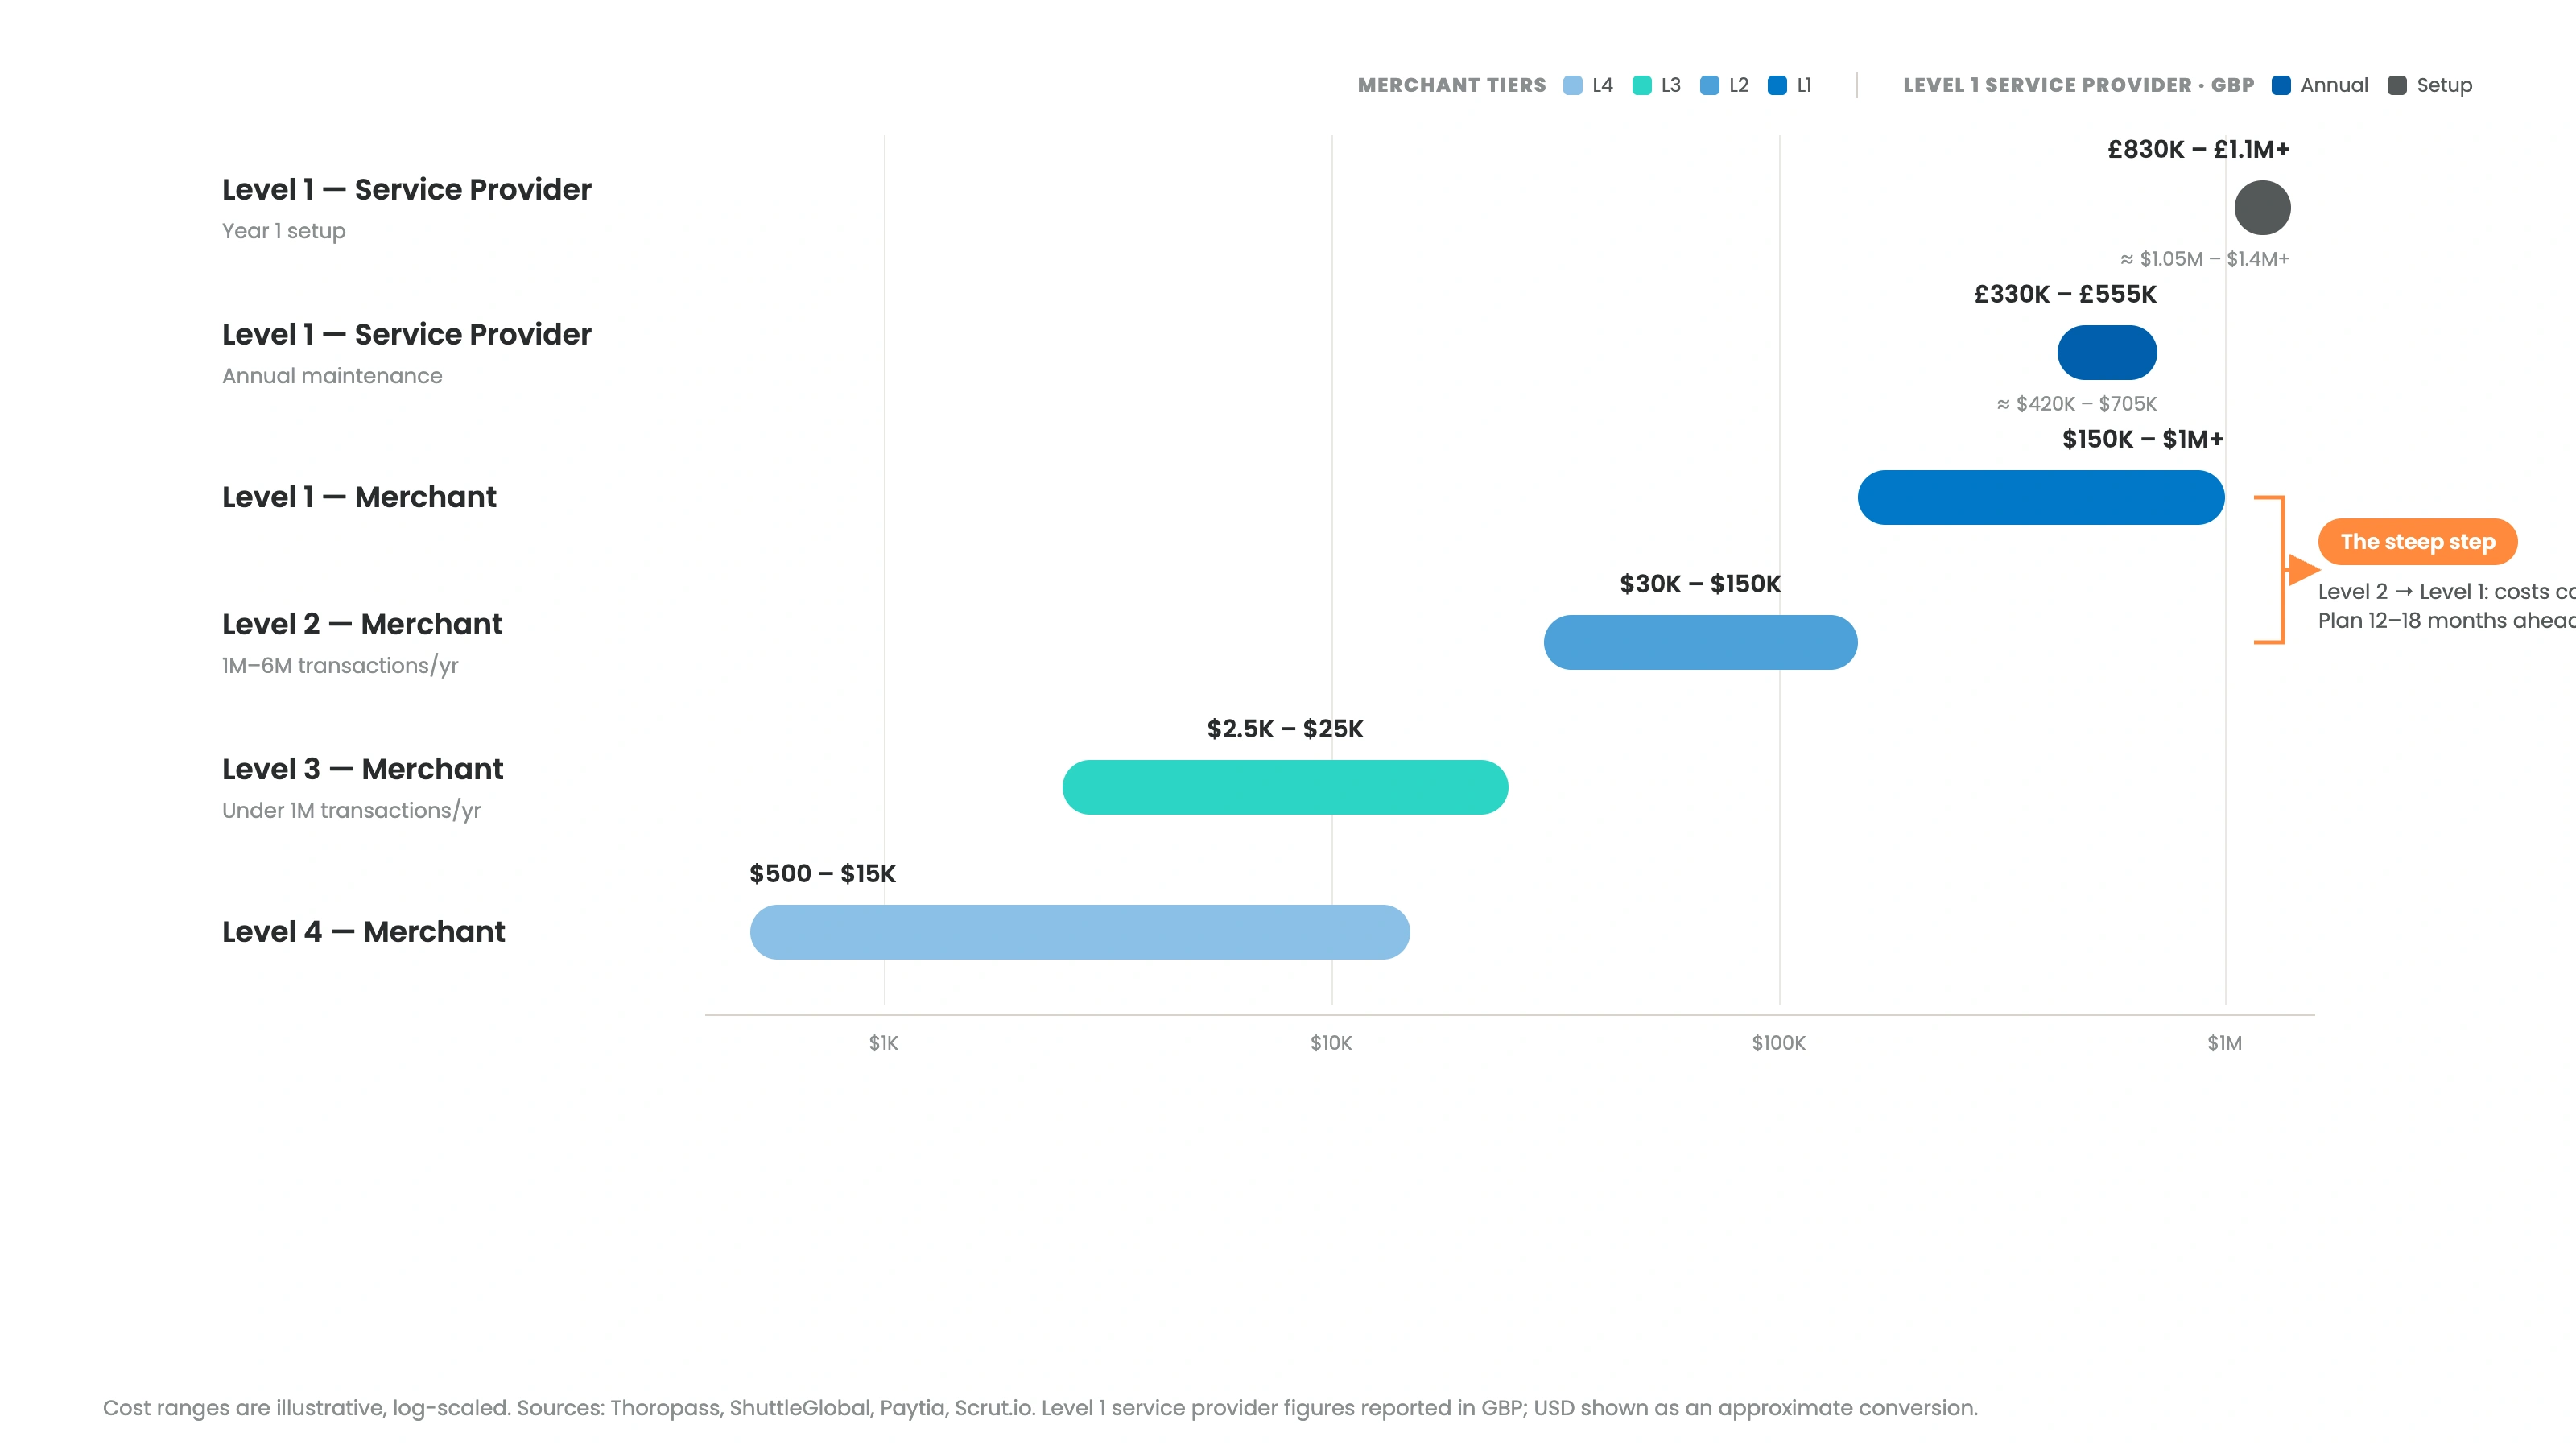
Sources: Secureframe, Thoropass, Shuttle Global, Paytia, Scrut.io
"The jump from Level 2 to Level 1 is steep. Platforms approaching the 300,000-transaction threshold should plan for the cost increase 12 to 18 months in advance."

Shuttle Global

The direct cost stack: tooling and continuous controls in 2026

An audit-ready environment runs on continuous tooling and operations, maintained year-round rather than assembled for a single assessment window. Technical controls consume 40% to 60% of an organization's total compliance budget.
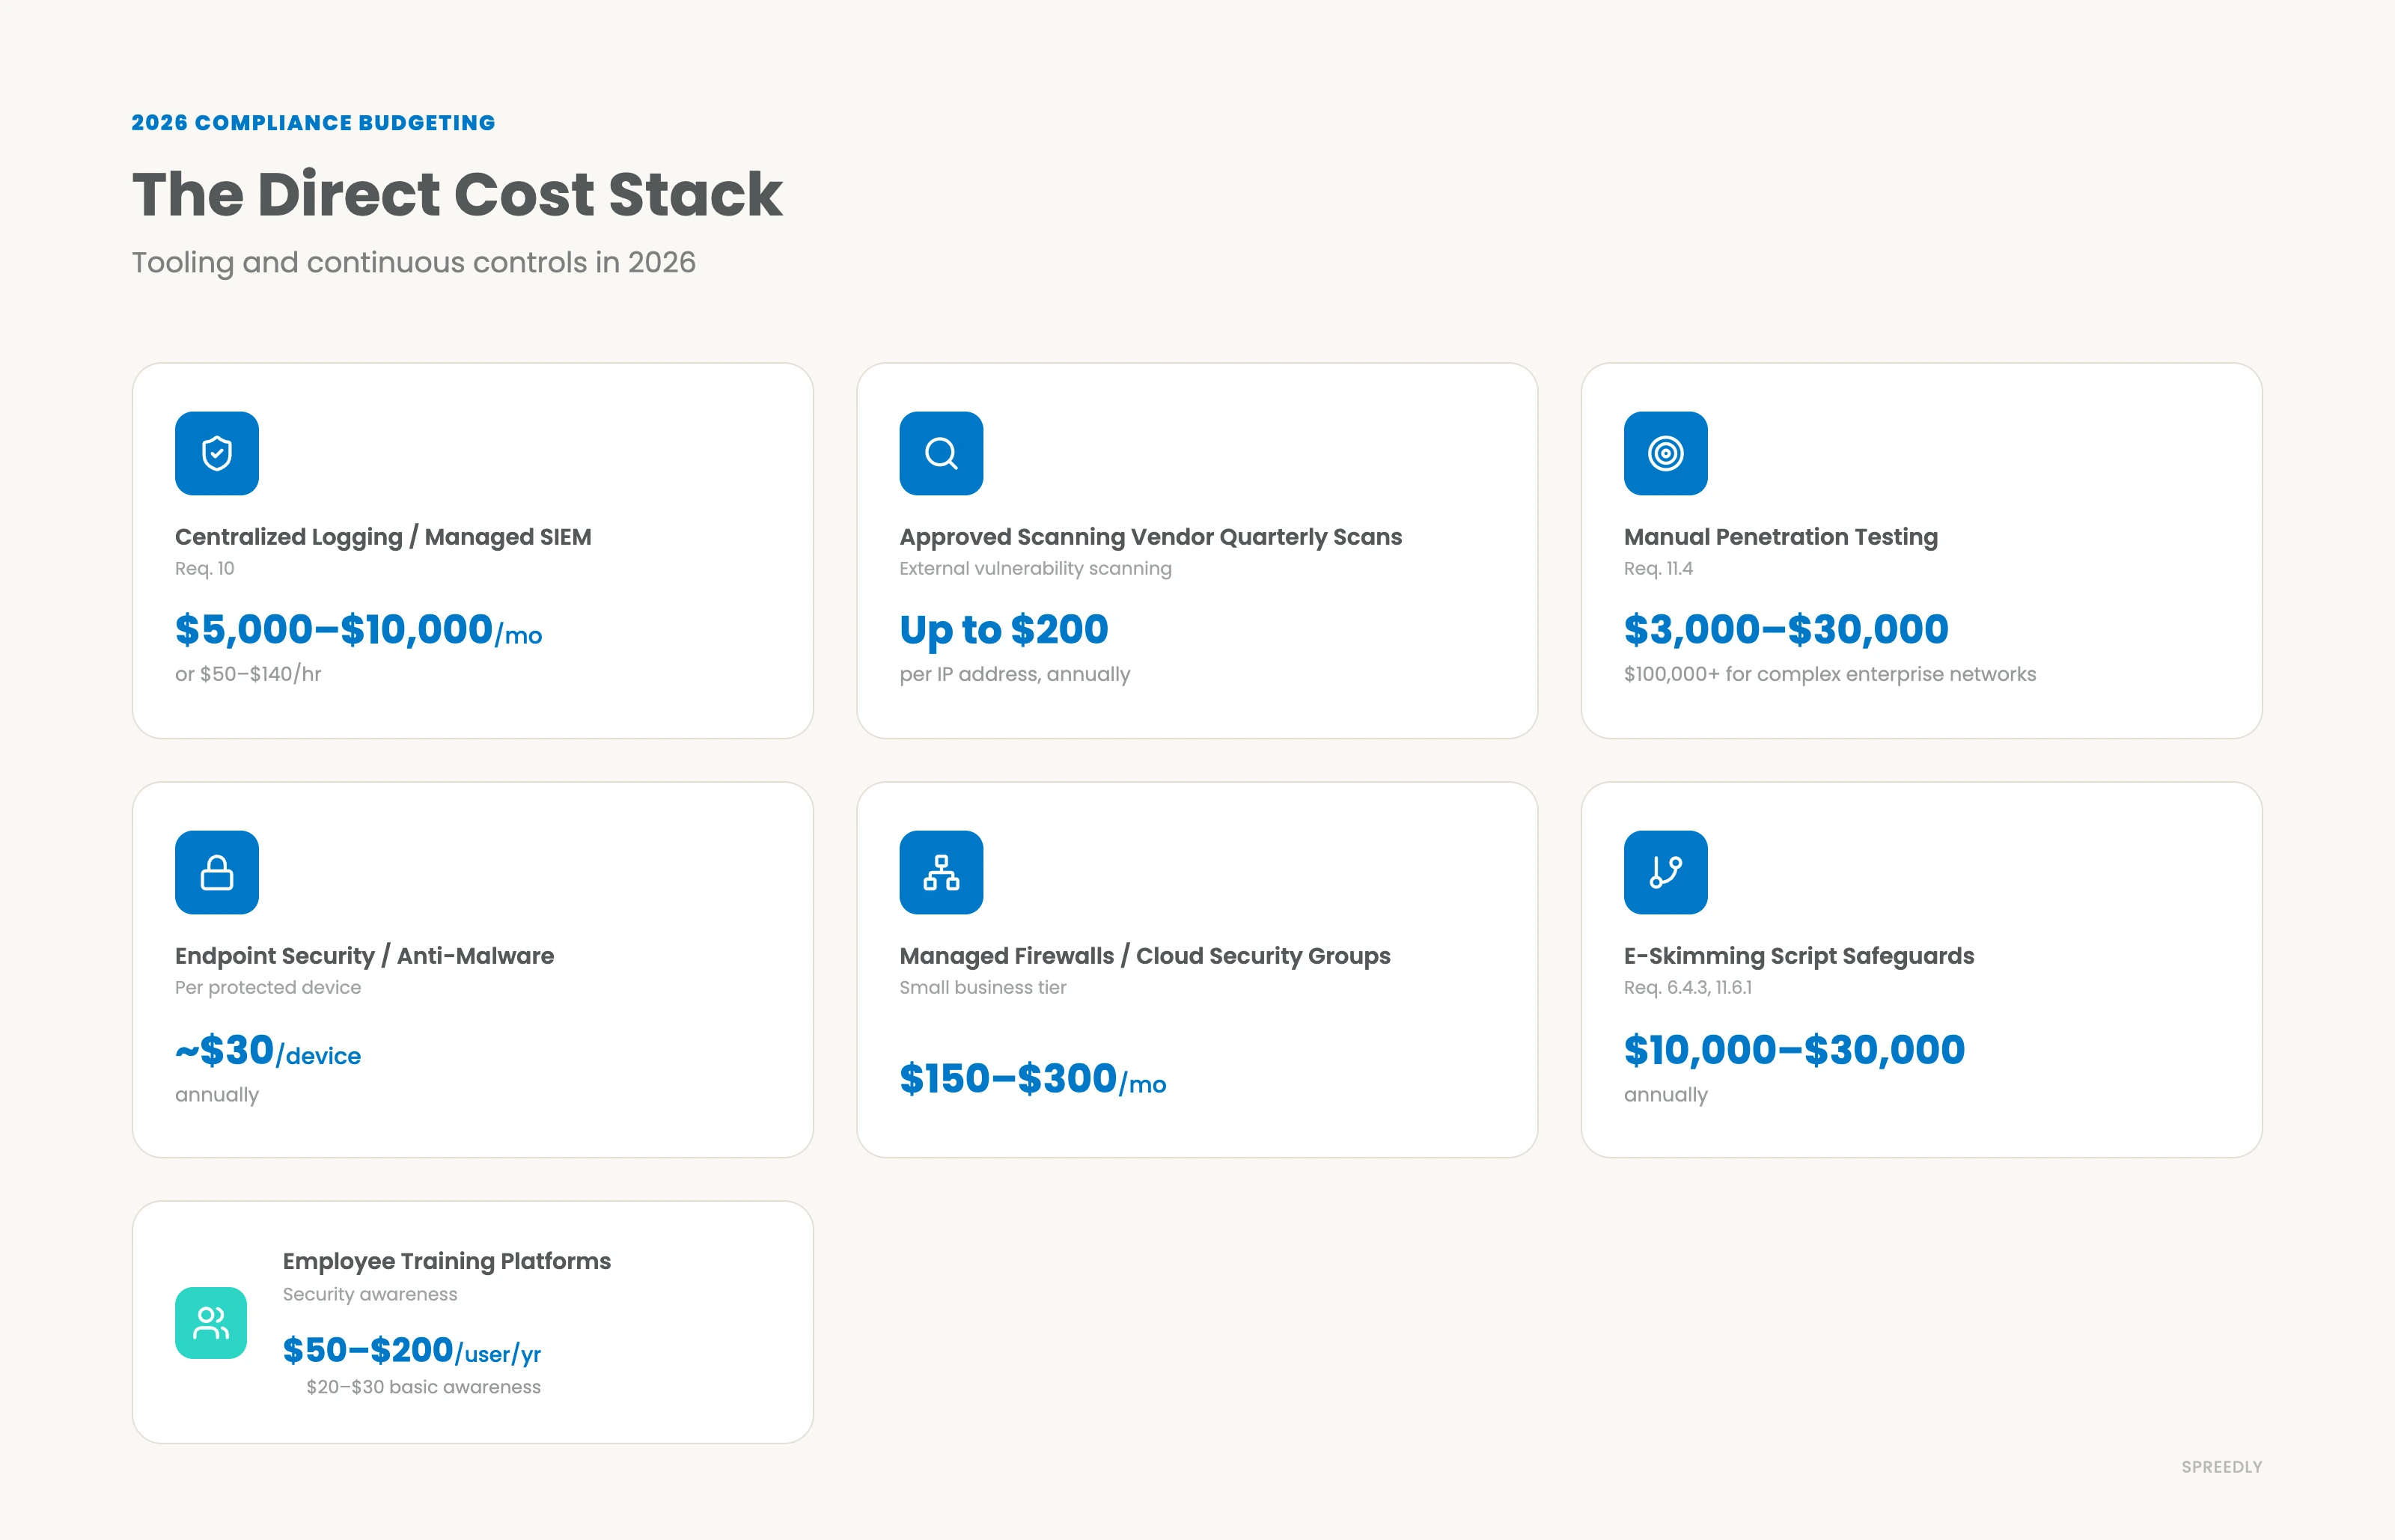
Sources: SecurityMetrics, SISA, FireCompass, Paytia
"Unlike automated scanning, penetration testing requires manual verification by experienced analysts. PTaaS replaces the annual engagement model with continuous, on-demand testing."

FireCompass

Scope reduction is the biggest lever you have

Network segmentation and data outsourcing are the most effective cost-saving strategy available to a compliance budget. Keeping primary account numbers out of the local network compresses audit surface area by 80% to 95%.

Outsourcing the web checkout. Which SAQ a merchant files depends on where the card number physically touches their systems. Build your own checkout form, and raw card data lands on your own servers, which pulls you into SAQ D, 300-plus questions.

Hand the card fields off to a hosted iframe instead, and that data never reaches your servers at all, which qualifies you for SAQ A, just 22 questions. Making that switch drops ongoing annual compliance cost to £5,000 to £15,000. For a platform running that checkout at scale, that is an immediate savings of £315,000 to £540,000 a year.

Outsourcing the contact center. Traditional phone-payment environments pull call recordings, CRM screens, and network routing into scope, at a cost upwards of £133,000 annually.

DTMF masking intercepts card details at the network edge before they reach the contact center, collapsing the CDE footprint and dropping annual compliance expense from £62,000 to £22,000, including software fees, a net savings of £40,000 a year.

"Scope reduction is the single most effective cost-saving measure. Implementing network segmentation to isolate cardholder data environments dramatically reduces your audit surface and QSA effort."

‍Thoropass

Both paths point to the same mechanism: get raw card data out of your environment before you count it as scope. Spreedly's Vault tokenizes cardholder data at capture so it never touches the merchant or platform's own systems, the same descoping logic behind the SAQ A and DTMF masking numbers above.

The acquirer or card brand still makes the final SAQ determination, per Spreedly's own guidance on SAQ eligibility, but the scope reduction itself is the lever.

What non-compliance actually costs

For financial officers, the price of non-compliance is layered, not a single number. The fine on a statement is only the first layer.

Six layers of liability:

  1. Acquiring bank monthly non-compliance fees, compounding over time: $5,000 to $10,000 a month for months one through three, $25,000 to $50,000 a month for months four through six, and $50,000 to $100,000 a month from month seven onward.
  2. Card brand enforcement fines: Mastercard SDP assessments up to $200,000 per violation, starting at $25,000 for a first violation; Visa AIS compromise-response penalties of $100,000 for Level 1 and 2 merchants; Visa Failure to Notify assessments up to $100,000 per incident for missing the three-calendar-day reporting window.
  3. PCI Forensic Investigations, mandated after a breach: investigators bill $200 to $500 an hour, with total forensic budgets of $25,000 to $200,000 or more, and cases that exceed $500,000.
  4. Per-card breach liabilities, passed down from issuing banks for reissuance and fraud losses: $3 to $10 per card at the low end, $20 to $50 mid-range, and $100 to $500 or more per card when prohibited data like CVVs or plain-text PINs was stored.
  5. Regulatory and legal exposure: GDPR fines up to 4% of annual global turnover for personal data breaches. Under Washington state law (RCW 19.255.020) and Minnesota law (Statutes 325E.64), merchants are legally liable to issuing banks for reissuance costs if reasonable care was not exercised.
  6. Hidden brand interruption: downgraded merchant interchange rates, rolling reserve requirements of 5% to 10% trapping working capital, voided cyber-insurance policies, and complete revocation of card processing privileges.
"There is no single fee. There is a layered set of charges that combine into a real total which routinely exceeds a hundred times the headline figure."

SecureCodingHub

How to budget for PCI compliance in 2026

Managing compliance spend effectively requires a proactive, structured capital allocation model. Continuity is the cheapest mode. Letting compliance lapse is twice as expensive to restart.

The 2026 compliance capital allocation matrix:
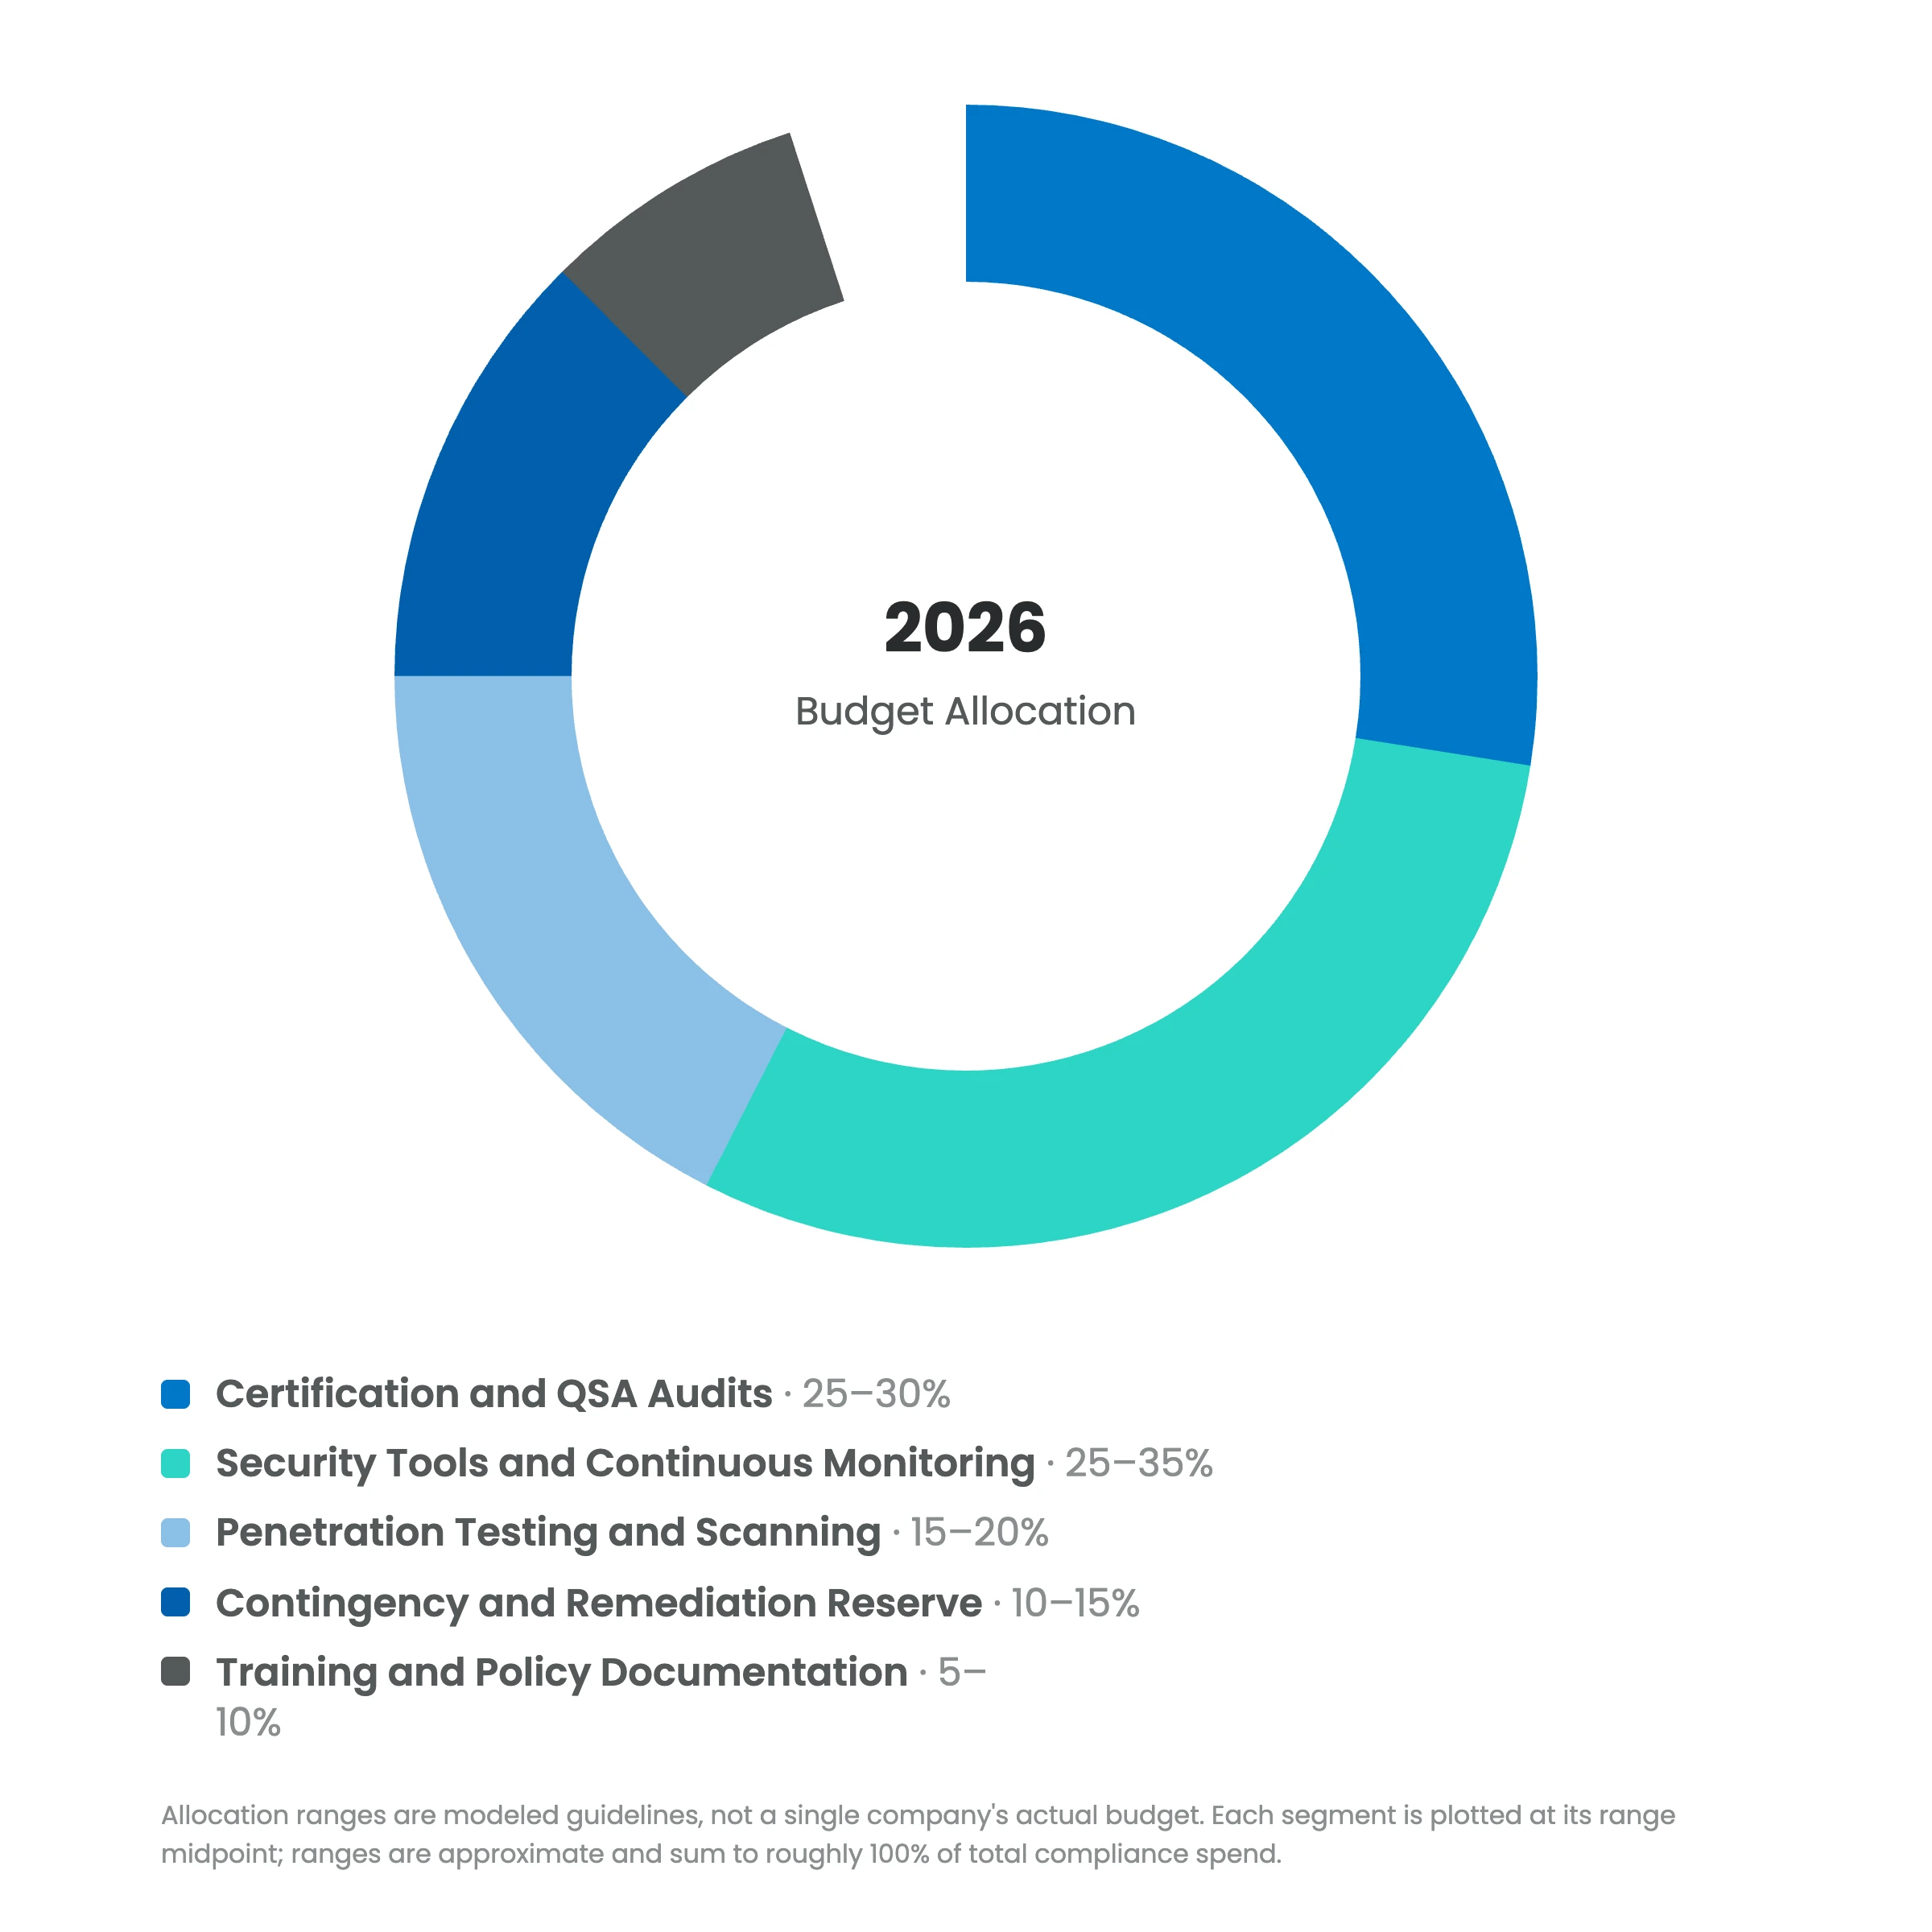
Sources: CompliancePoint, FireCompass, SecureCodingHub, SecurityMetrics
"Compliance investments compound. A program that maintains the AOC every year, runs the scans every quarter, and trains the personnel every cycle produces evidence as a continuous byproduct. Continuity is the cheapest mode."

‍SecureCodingHub

‍

"The road to PCI DSS v4.0.1 compliance is a marathon, not a sprint. The key is to be methodical and strategic."

SecurityMetrics

Turn compliance into a competitive advantage

PCI DSS compliance under version 4.0.1 is an ongoing operational commitment that builds customer trust and protects business margins.

Three steps matter more than the rest:

  1. Run an urgent gap assessment against the 4.0.1 standard.
  2. Map CDE boundaries to stop silent scope creep.
  3. Descope high-liability paths like voice and e-commerce checkout to qualify for simplified SAQ A validation.

That third step is where Spreedly's hosted tokenization comes into play: card data is captured and vaulted before it ever reaches your servers, which is what makes the SAQ A path available in the first place. Pair that with payment data security practices across the rest of the stack, and the compliance line item stops growing every time the standard does.

Support Portal

Spreedly Support
Trust Center
Platform Status

Developer Portal

Developer Guides
Documentation
Read more
Written By
How much does PCI compliance cost per year?

Anywhere from $1,000 to $50,000 or more, depending on your transaction volume, your PCI compliance level, and how much of the validation work you outsource versus handle in-house. A small Level 4 merchant filling out a self-assessment questionnaire pays far less than a Level 1 enterprise running a full on-site assessment.

What are the four PCI compliance levels?

Card networks sort merchants by annual transaction volume. Level 1 covers more than 6 million transactions a year, Level 2 covers 1 million to 6 million, Level 3 covers 20,000 to 1 million, and Level 4 covers fewer than 20,000. Your level decides how you validate compliance, and validation is where most of the cost lives.

Do I need a third-party assessor, or can I self-assess?

Level 1 merchants must hire a Qualified Security Assessor (QSA) to complete a Report on Compliance (ROC). Levels 2 through 4 can typically self-validate with an Annual Self-Assessment Questionnaire (SAQ), though many hire an assessor anyway since a QSA tends to catch gaps before they turn into fines.
Download Free
Get My Report
Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.
Learn More
Download Free
Get My Report
Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.

Written by

Rachel Fine

Rachel Fine is Senior Compliance Manager at Spreedly, where she leads the company’s PCI-DSS and SOC 2 compliance programs and oversees governance frameworks that support secure, scalable payment infrastructure. Her work focuses on translating regulatory requirements into practical, risk-based processes that enable the business to move confidently while maintaining strong security and audit readiness.

Rachel brings a structured, program-driven approach to compliance, balancing strategic oversight with operational detail. She has guided initiatives spanning PCI DSS 4.0 readiness, data classification, SOC 2 certification, and customer advisory on regulatory obligations, helping organizations navigate evolving standards without slowing innovation.

Rachel writes about payment compliance, PCI DSS, SOC 2, and regulatory strategy, with a focus on helping organizations understand the real cost of compliance, reduce development burden, and build resilient governance programs that support long-term growth.

Lorem Ipsum Dolor Sit

Vel sed vitae enim nec suspendisse ut viverra tincidunt quis

Learn More

Related Articles

Addressing New PCI DSS 4.0 Security Concerns With Payments Orchestration

Payment Security

Rachel Fine

November 22, 2023

Arc'teryx and the 2019 PSD2 Mandate

Payment Security

Lorra Gosselin

June 23, 2020

Benefits of Performing Security Risk Assessments

Payment Security

Aaron Finley

June 15, 2022

Back to Blog

Get Regular Updates From Payments Experts

Subscribe to our newsletter and we’ll send you a monthly update of all of our new content so you don’t miss out on new data, new insights, and news from the world of payments. 

Insights and updates you actually care about

Get practical, actionable insights written by experts from the world of digital payment solutions delivered to your Inbox.

By subscribing, you agree to our Privacy Policy and Terms.

Find Us On

Company
  • Pricing
  • About
  • Careers
  • Contact Us
  • Partners
Resources
  • Support
  • Blog
  • Guides
  • News
  • Webinars
  • Trust Center
Developers
  • Developer Guides
  • Documentation
  • See Demo
  • Status

Find Us On

Privacy SettingsTermsPrivacyStatus
© 2026 Spreedly, Inc. All rights reserved.