




A card tokenization failure can start in the payment form, at the token service provider or in the vault, and the error message rarely says which. That makes these failures slow to diagnose.
Card-on-file payments run on tokens, and Mastercard plans to tokenize all of its ecommerce transactions in Europe by 2030. Visa's April 2026 fee changes also raised the cost of the token services behind card-not-present transactions, so a failure that needs a retry or a fix costs more than it did.
This post covers what a tokenization failure is, what "tokenization service denial" and "error tokenizing card number" mean, the five common causes, what a failed token costs, and how Spreedly reduces failures at each point.
What are card tokenization failures?
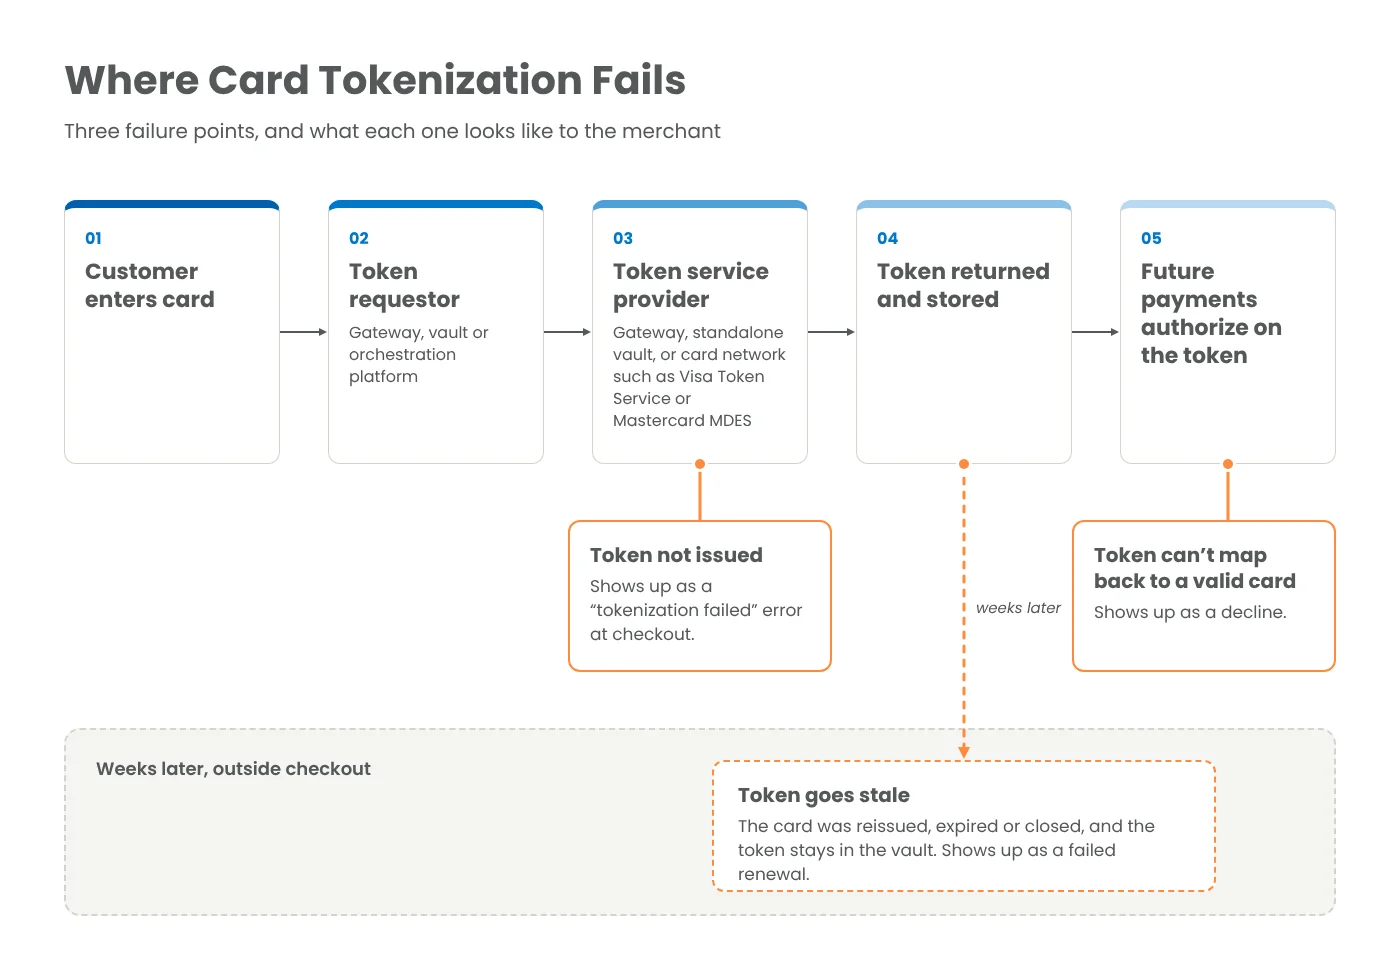
Tokenization swaps a primary account number (PAN) for a token, a stand-in value that's worthless outside the system that issued it. A card tokenization failure is any point where that swap doesn't happen or stops holding up. The token never gets created, it gets created but can't be mapped back to a valid card, or a token that worked last month no longer resolves because the card behind it changed.
The first two show up at checkout as an error or a decline. The third is harder to catch. A stored card goes stale in the vault, and nobody notices until a renewal fails.
How card tokenization works
When a customer enters a card, the token requestor (your gateway, vault or orchestration platform) sends the card details to a token service provider. That provider can be a gateway, a standalone vault, or a card network running its own service, such as Visa Token Service or Mastercard MDES. The provider returns a token, and future transactions carry the token instead of the PAN. Only systems with the right access can map it back to the card.
There are two kinds of tokens in most payment stacks. PCI tokens are issued by the vault that stores the card, and a token tied to a single gateway's vault can't follow the card to another processor. Network tokens are issued by the card networks and stay valid when a card is reissued, because the network updates the credential behind the token. The two work together: a PCI token for storage and portability, and a network token for authorization wherever the gateway supports it.
Every handoff in that chain is a place where tokenization can fail.
Debit vs. credit card tokenization
Debit and credit cards are tokenized the same way, through the same token services. The difference is in what a failure costs. A debit card draws on a bank account. When it's stored for recurring charges like a subscription, a utility bill or rent, and the token fails on a renewal, there's usually no customer at the keyboard to re-enter the card, so the payment simply doesn't happen until someone follows up.
Credit card tokens fail for the same reasons. Whatever the card type, the fix is the same: keep tokens in sync with the card's real status before the next charge.
What is tokenization service denial?
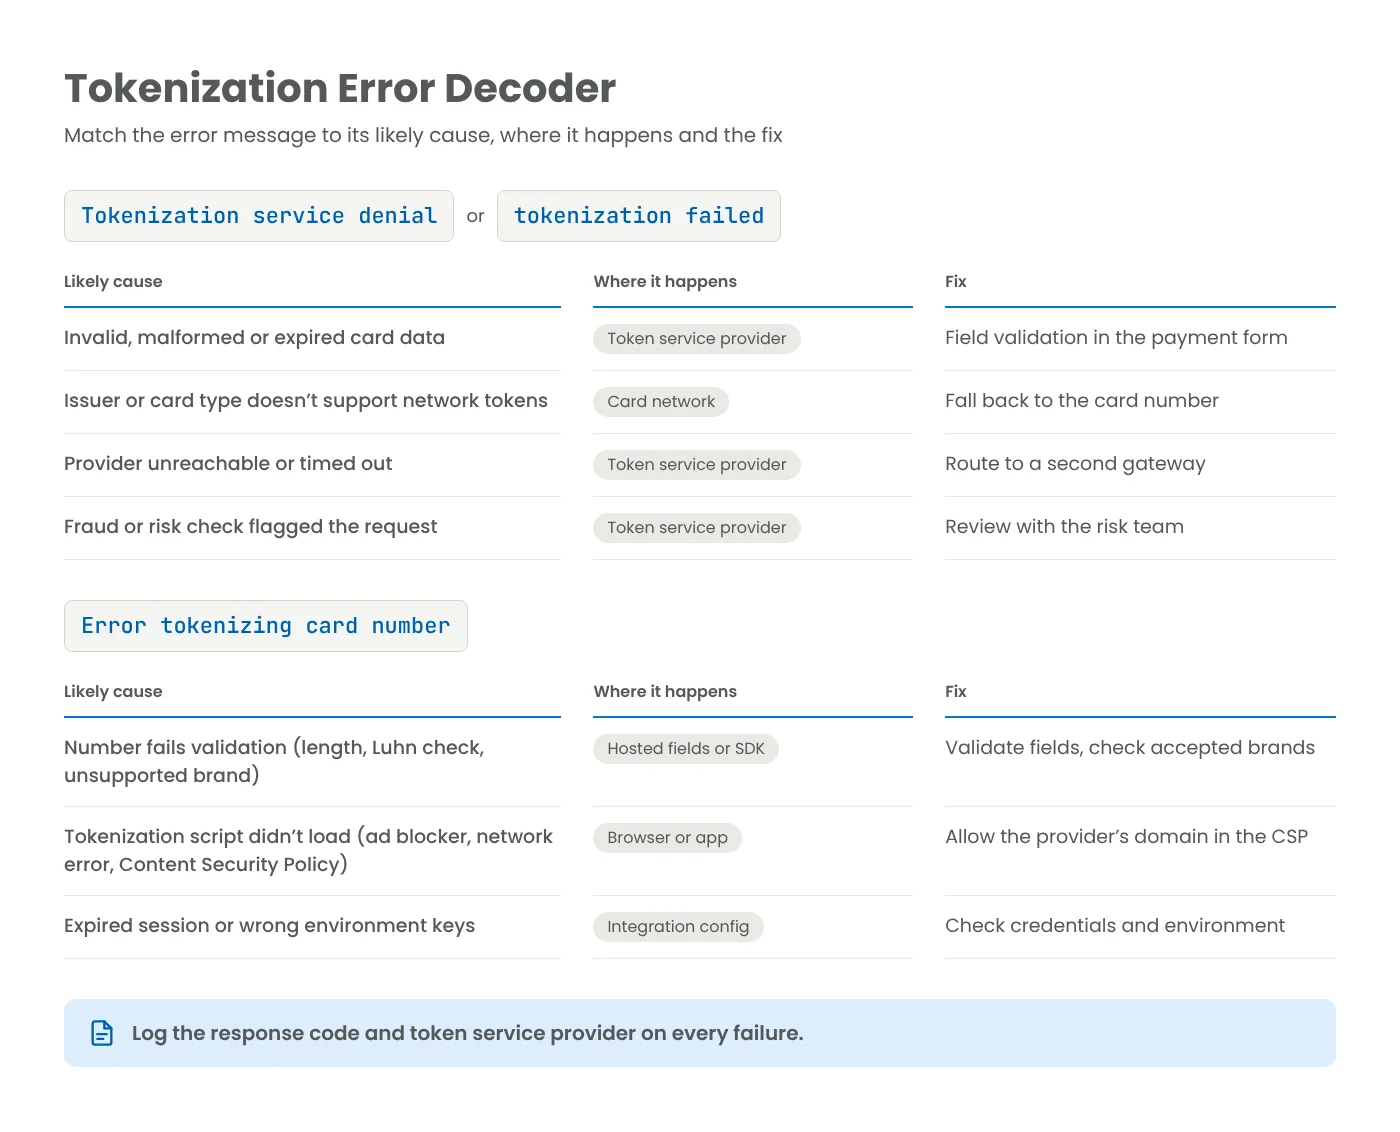
A "tokenization service denial" or "tokenization failed" message means the token service provider refused or couldn't complete the request. It usually happens at payment initiation, when the card is first tokenized. The most common reasons:
- The card data was invalid, malformed or expired.
- The card's issuer or card type doesn't support network tokens yet, or the network couldn't provision one.
- The token service provider was unreachable or timed out.
- A fraud or risk check flagged the request.
The message alone rarely tells you which one you're dealing with. Log the response code and the token service provider on every denial so you can separate a bad card from a provider outage, then route the fix to the right team.
Error tokenizing card number
This error usually comes from hosted payment fields or a checkout SDK, when the card number can't be converted to a token before it leaves the browser or app. Three things cause most of them.
The number fails basic validation. It's the wrong length, fails the Luhn check, or belongs to a card brand the integration isn't set up to accept.
The tokenization script never loaded. Ad blockers, network errors and Content Security Policy rules can all stop it. Under PCI DSS v4.0.1, Requirement 6.4.3 requires merchants to authorize, integrity-check and inventory every payment page script. A script policy tightened for compliance that leaves out the tokenization provider's domain will break tokenization for every customer.
The session or environment credentials are wrong. Expired session tokens or keys pointing at the wrong environment cause tokenization requests to be rejected before they reach the provider.
Common causes of tokenization failures
Outside of checkout-specific errors, most tokenization failures trace back to five causes.
Network and system interruptions
Gateway downtime, timeouts between the token requestor and the token service provider, or an outage at the card network can break the handoff before a token is issued. These failures cluster. When one provider goes down, every transaction routed to it fails until traffic moves somewhere else.
Inaccurate card data
Typos in the card number, mismatched expiration dates and missing billing details get rejected by systems built to catch exactly that. Field-level validation in the payment form catches most of these before the request is ever sent.
Security and compliance controls
PCI DSS v4.0.1 has been fully in force since March 31, 2025, when the requirements the PCI Security Standards Council had future-dated became mandatory. Two requirements touch tokenization directly. Requirement 3.5.1 says PAN must be unreadable anywhere it's stored, and lists index tokens as one accepted method. Requirement 6.4.3 covers the payment page scripts that tokenization often depends on. A vault or checkout flow that misses either one can fail an assessment, and the controls themselves can cause failures if they're configured without the tokenization flow in mind. Tokenization also shrinks your PCI compliance scope, which is why getting it right pays off beyond the transaction.
Invalid and expired cards
Cards expire, get reissued after a breach, or get closed. If tokens don't track the card's status, a token that worked last month stops working this month. These dead credentials, or zombie tokens, stay in the vault, keep adding to vault costs, and can no longer authorize a payment.
Duplicate cards
The same customer can store the same card more than once: at signup, again after a failed payment, again on a new device. Each duplicate is another token to maintain and update, and a stale copy can get charged instead of the current one. Detecting duplicates at the point of storage keeps the vault clean and keeps charges going to the right credential.
What is the cost of a failed token?
The direct cost is the transaction. A failed token means a failed authorization and, in a live checkout, a customer who has to try again. Some will. Others will assume your checkout is broken and buy somewhere else. On stored-card and recurring payments, the cost builds because every failure needs remediation: a retry, a dunning email, a support ticket, or a request for the customer to re-enter their card.
The cost of accepting cards also went up in April 2026. Payments-cost firm CMSPI estimates the April 2026 U.S. network fee changes could cost merchants up to $3 billion, and up to roughly $900 million of that comes from three Visa changes tied to tokens:
- The Digital Commerce Service Fee now applies to card-not-present authorizations, and it bundles several token and credential services into one fee, including token authentication verification and Visa Account Updater. CMSPI estimates about $122 million in added cost.
- The Digital Commerce Authentication Program added a 5 basis point network fee and reduced the interchange benefit merchants earn on network-tokenized transactions. CMSPI estimates up to $771 million a year.
- A new Card-Present Token Fee applies to network-tokenized card-present transactions, at about $15 million a year.
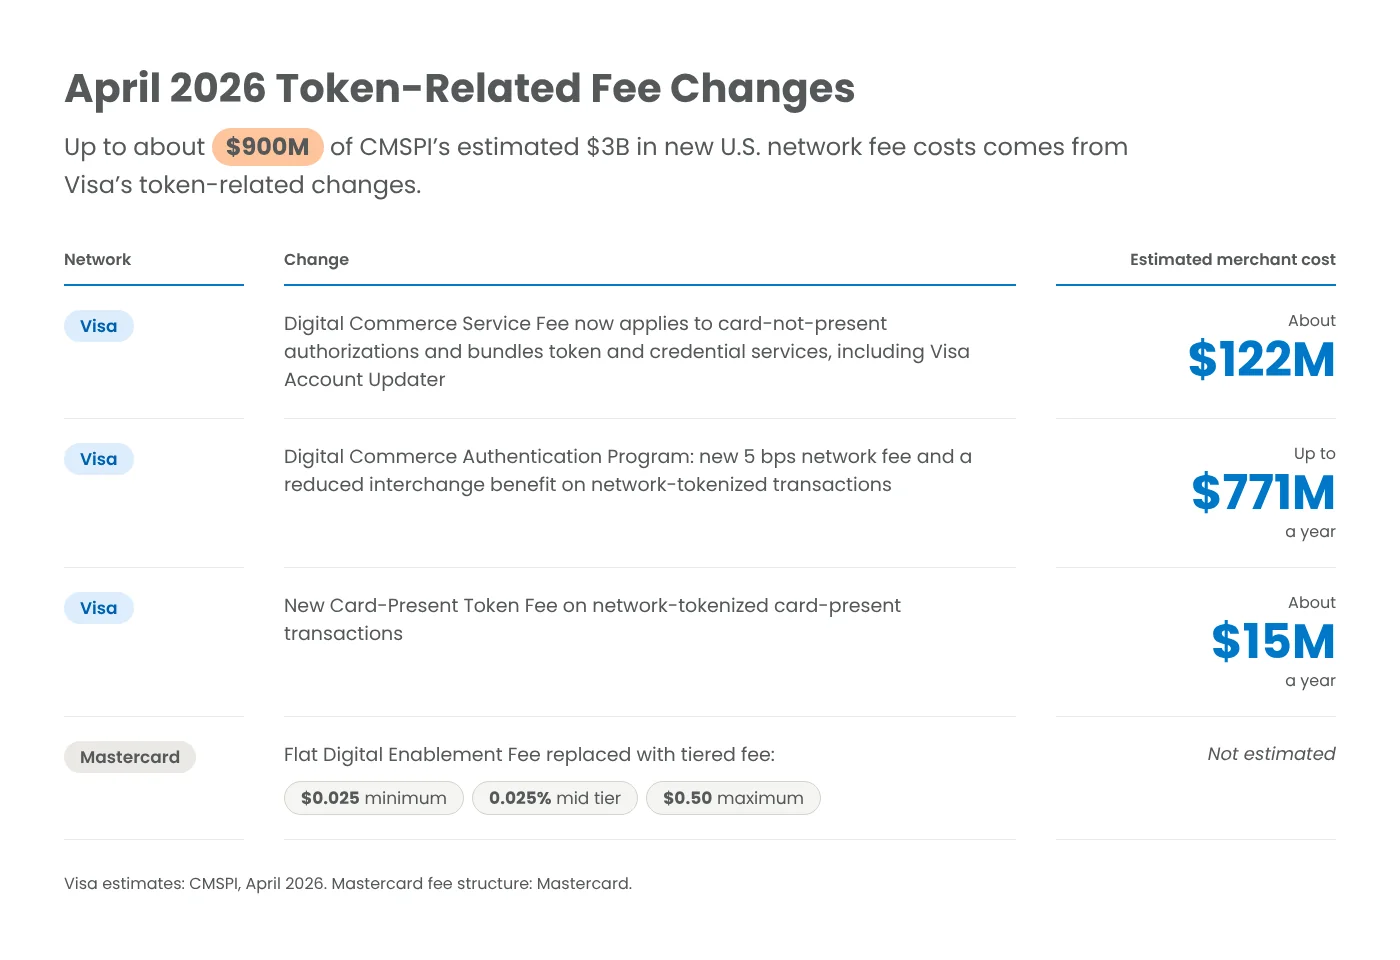
Mastercard also replaced its flat Digital Enablement Fee on card-not-present transactions with a tiered fee: a $0.025 minimum, 0.025% of the transaction amount in the middle tier, and a $0.50 maximum.
Network tokens still lift authorization rates and reduce fraud exposure. But with more of the cost of tokenization built into network fees, a token that fails and has to be retried, fixed or replaced costs more than it did before these changes.
How Spreedly reduces tokenization failures
Spreedly addresses each of those causes at a different layer of the payment stack.
Provider outages and timeouts are a routing problem. Transaction routing in Spreedly Optimize, built in Composer, sends each transaction to the best-fit gateway based on rules you set, and can split volume across more than one gateway. Routing changes take effect as soon as you publish them, with no code deploy, so moving traffic off a gateway that's having problems is a rule change your payments team can make on its own.
Bad card data is caught earlier with verification. Adding a card to the vault doesn't validate it, so a Verify transaction runs a small authorization and void through your gateway to confirm the card can be charged. Problems surface at enrollment instead of at the first renewal.
Stale and expired cards are handled by Advanced Vault. Spreedly tokens aren't tied to a single gateway, so a gateway switch or outage doesn't mean re-tokenizing your customer base. Advanced Vault adds lifecycle management for Visa, Mastercard and Discover cards, with twice-monthly batch updates, real-time Mastercard updates and on-demand Visa inquiries. It provisions network tokens for eligible cards and falls back to the card number automatically when a network token can't be used, so a token problem doesn't turn into a decline. It also unenrolls stale credentials automatically, so you stop paying to update cards you'll never charge.
Duplicates are flagged with card fingerprints. Every card stored at Spreedly gets a fingerprint, and cards with the same PAN in the same environment share it, which makes duplicate payment methods easy to find and clean up.
Get ahead of card tokenization failures
Mastercard reports that three in five of its ecommerce transactions in Europe are now tokenized, and it's working toward 100% ecommerce tokenization in Europe by 2030. As that share grows, more of your payment failures will start as tokenization failures.
Track tokenization failure rate as an operating metric next to authorization rate and fraud loss. Break failures out by cause (card data, provider availability, card lifecycle) and by token service provider, give the metric an owner, and review it on a set cadence.
To see how a portable, network-token-ready vault cuts tokenization failures, talk to our team or learn more about Spreedly Vault.

What is a card tokenization failure?

A card tokenization failure occurs when card details cannot be successfully tokenized. Tokenization is the process of substituting sensitive card data with a unique, non-sensitive equivalent called a token. When this system fails, it not only jeopardizes the current transaction but can also expose sensitive cardholder data to potential security threats.
How does credit card tokenization work?
The card details go to a token service provider, such as a vault, a gateway or a card network, which returns a token. Your systems store the token and send it with each payment. Only systems with the right access can map it back to the card number.
How do you fix a card tokenization failure?
Start with the cause. Bad card data needs field validation in the payment form. Provider outages need a second gateway you can route to. Stale stored cards need lifecycle management or network tokens to keep them current. Script errors in hosted payment fields usually mean a Content Security Policy is blocking the tokenization script.